
Ammolite Insights: October 15, 2026
CYBERSECURITY NEWS, INSIGHTS & ANALYSIS
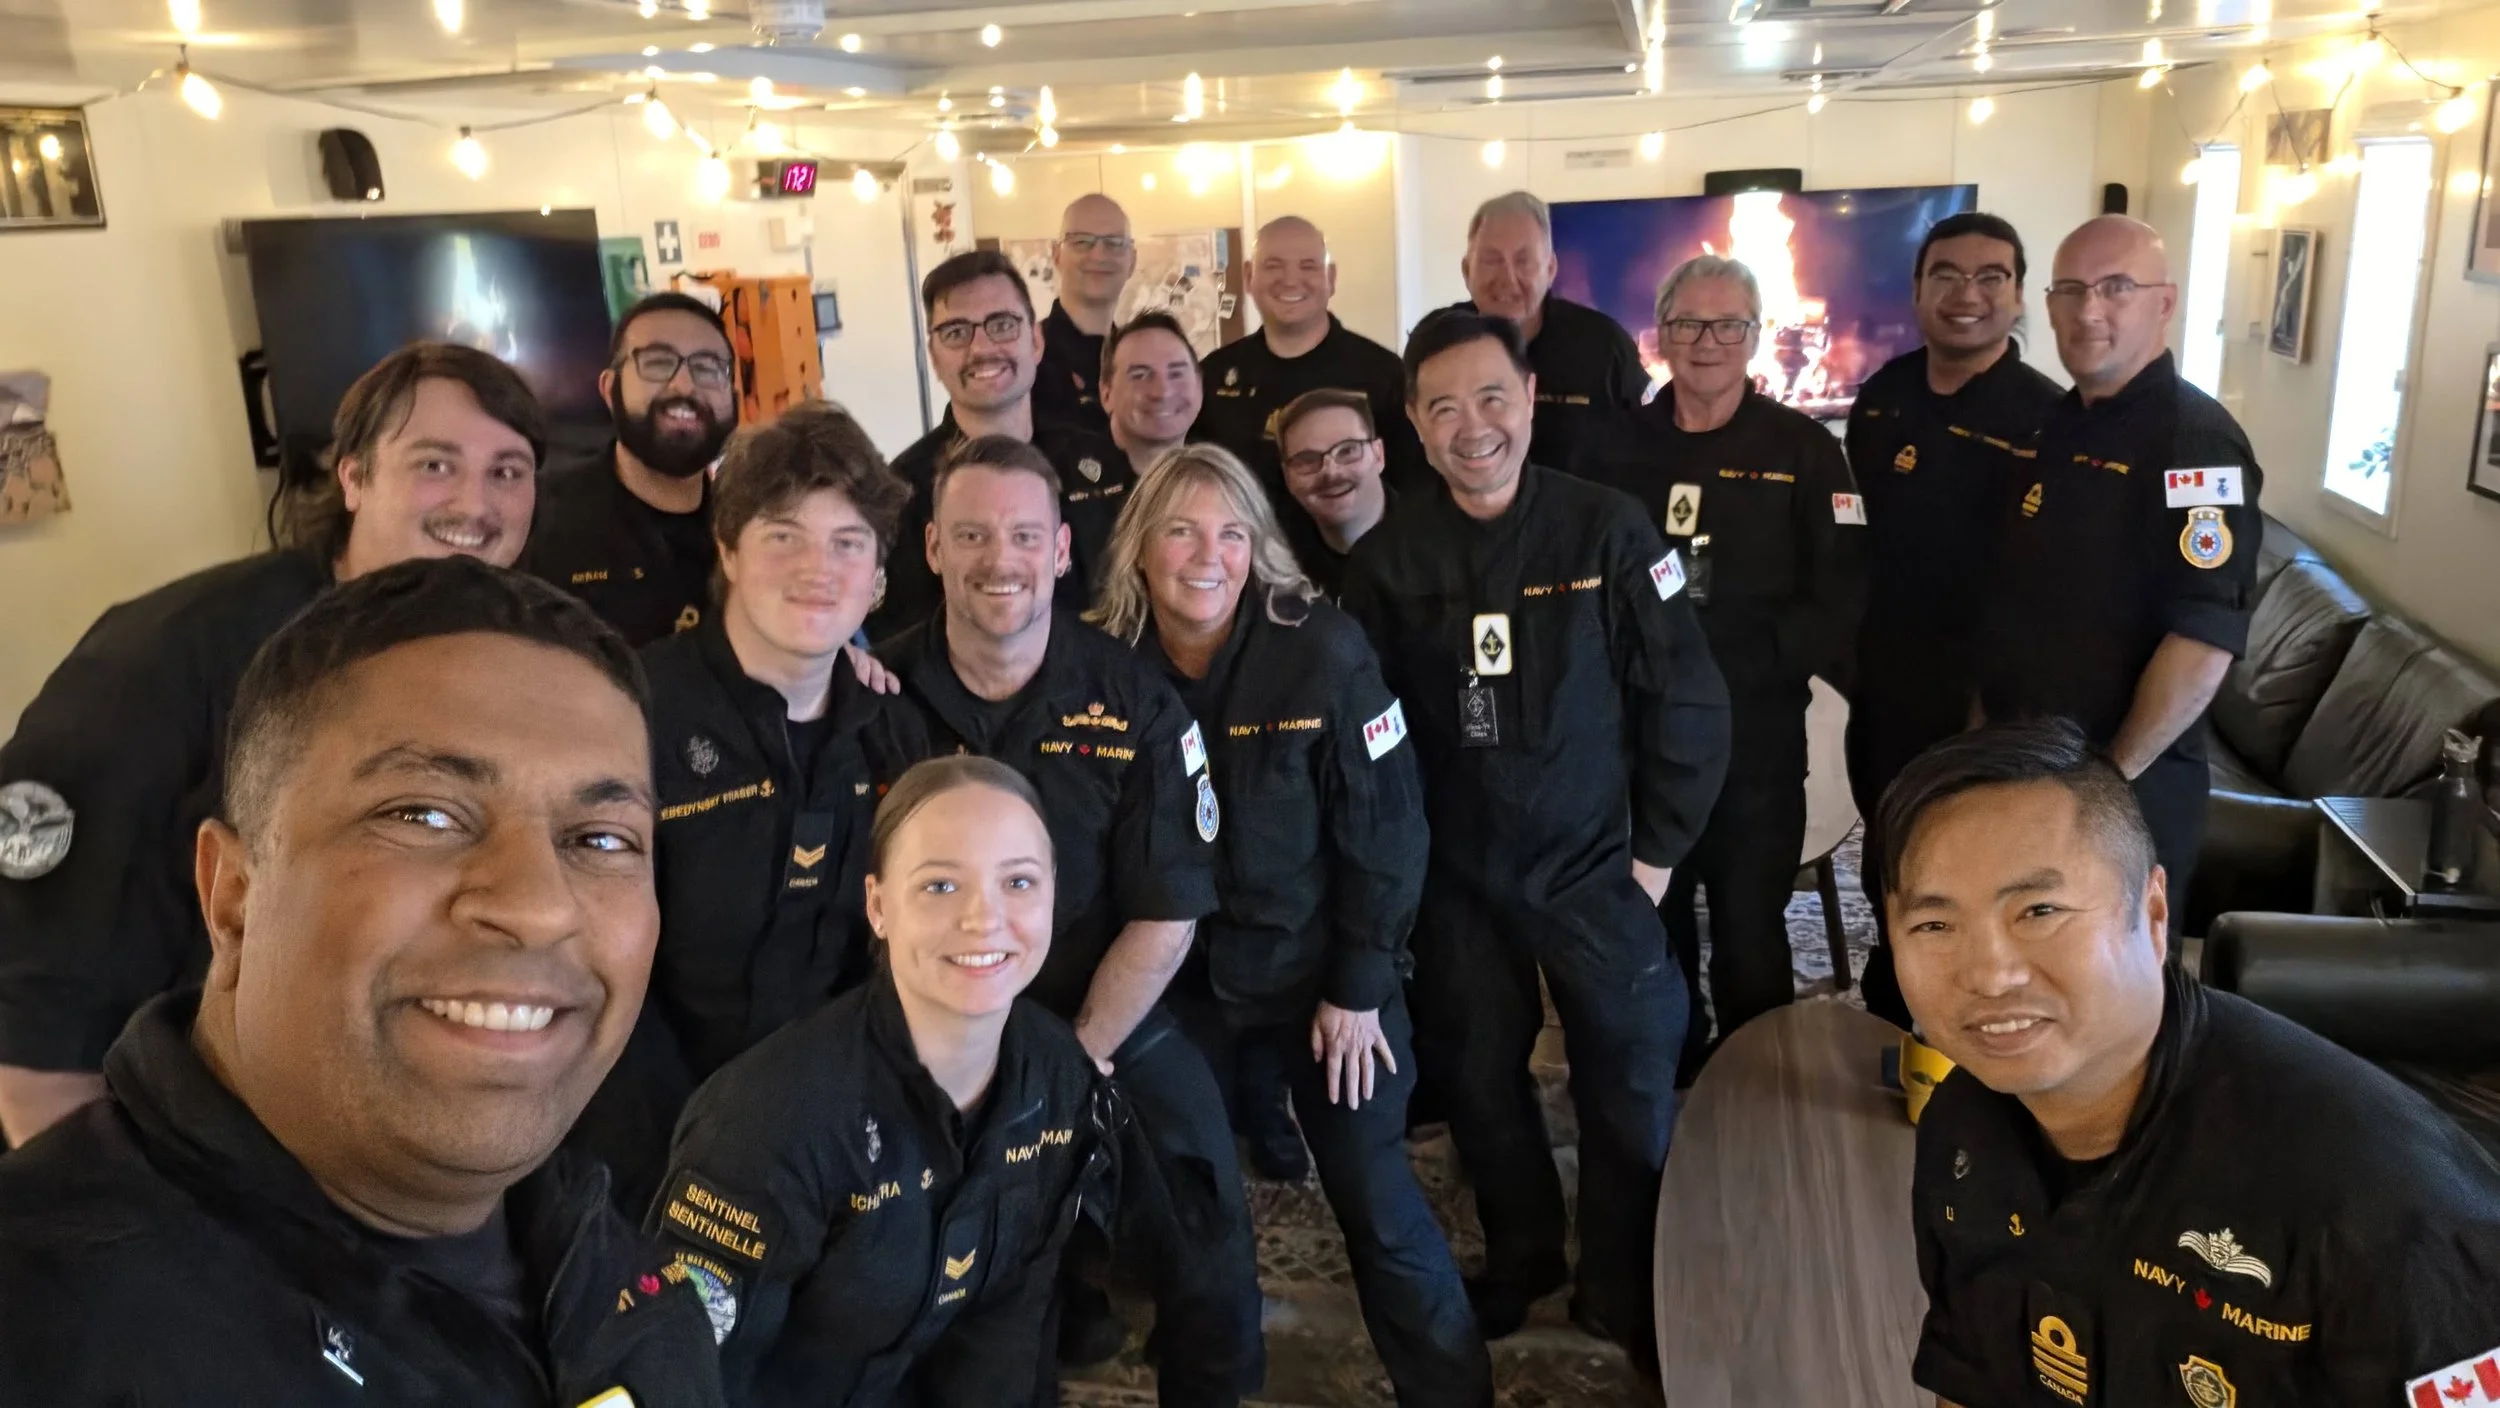
Leadership at Sea: Lessons from the Royal Canadian Navy
In September, Ammolite Security CEO Cara Wolf had the opportunity to participate in the Royal Canadian Navy’s Canadian Leaders at Sea (CLaS) program aboard HMCS Max Bernays.
Sailing from Prince Rupert to Vancouver, Cara gained a firsthand look at naval operations, leadership, communication, technology, and workforce development.
The experience reinforced several principles that have direct parallels with executive and board leadership: the importance of trusting expertise, creating clear accountability, and making disciplined communication part of how an organization operates.
“Strong leadership is not about one person having all the answers. It is about building capable teams, creating clarity, and ensuring that people have the confidence and authority to perform their roles.”
In The News
RCMP 'Monitoring' Reports of Massive North American Drivers' Licence Hack
The Royal Canadian Mounted Police says it is "aware" of an ongoing FBI investigation into a report that hackers gained access to tens of millions of government-issued identity records across North America, including Canadians' driver's licences.

Chinese Government-linked Cyber Threat Actors Combine Automated and Hands-on Hacking Tools to Steal Sensitive Data
Integrity Technology Group, a China-based company with links to the Chinese government, enables China-linked threat actors to exploit US and foreign organizations' networks across multiple sectors using various tools and techniques.
Mass Exploitation of Citrix NetScaler: What We Currently Know
Suspected state-linked actors targeted critical vulnerabilities in the widely used platform, causing widespread disruption across Europe and North America.
With new vulnerabilities, emerging technologies, and evolving threats competing for attention, it can be difficult to know where your organization should focus first.
Ammolite Security's Cybersecurity Assessments help organizations understand their current security posture, identify vulnerabilities, and prioritize the risks that matter most.
Our experts evaluate your organization's technology, operations, processes, and policies to identify gaps and provide practical recommendations for strengthening security and building long-term resilience. Assessments can also help organizations understand requirements under frameworks and standards, including CMMC, CPCSC, ISO 27001, NERC CIP, HIPAA, and PCI DSS.
The goal isn't simply to find what's wrong. It's to give you a clear path forward.